Improve the active and passive Burp Suite scanner by means of custom rules through GUI.
Searches code from over a half million public repositories on GitHub.
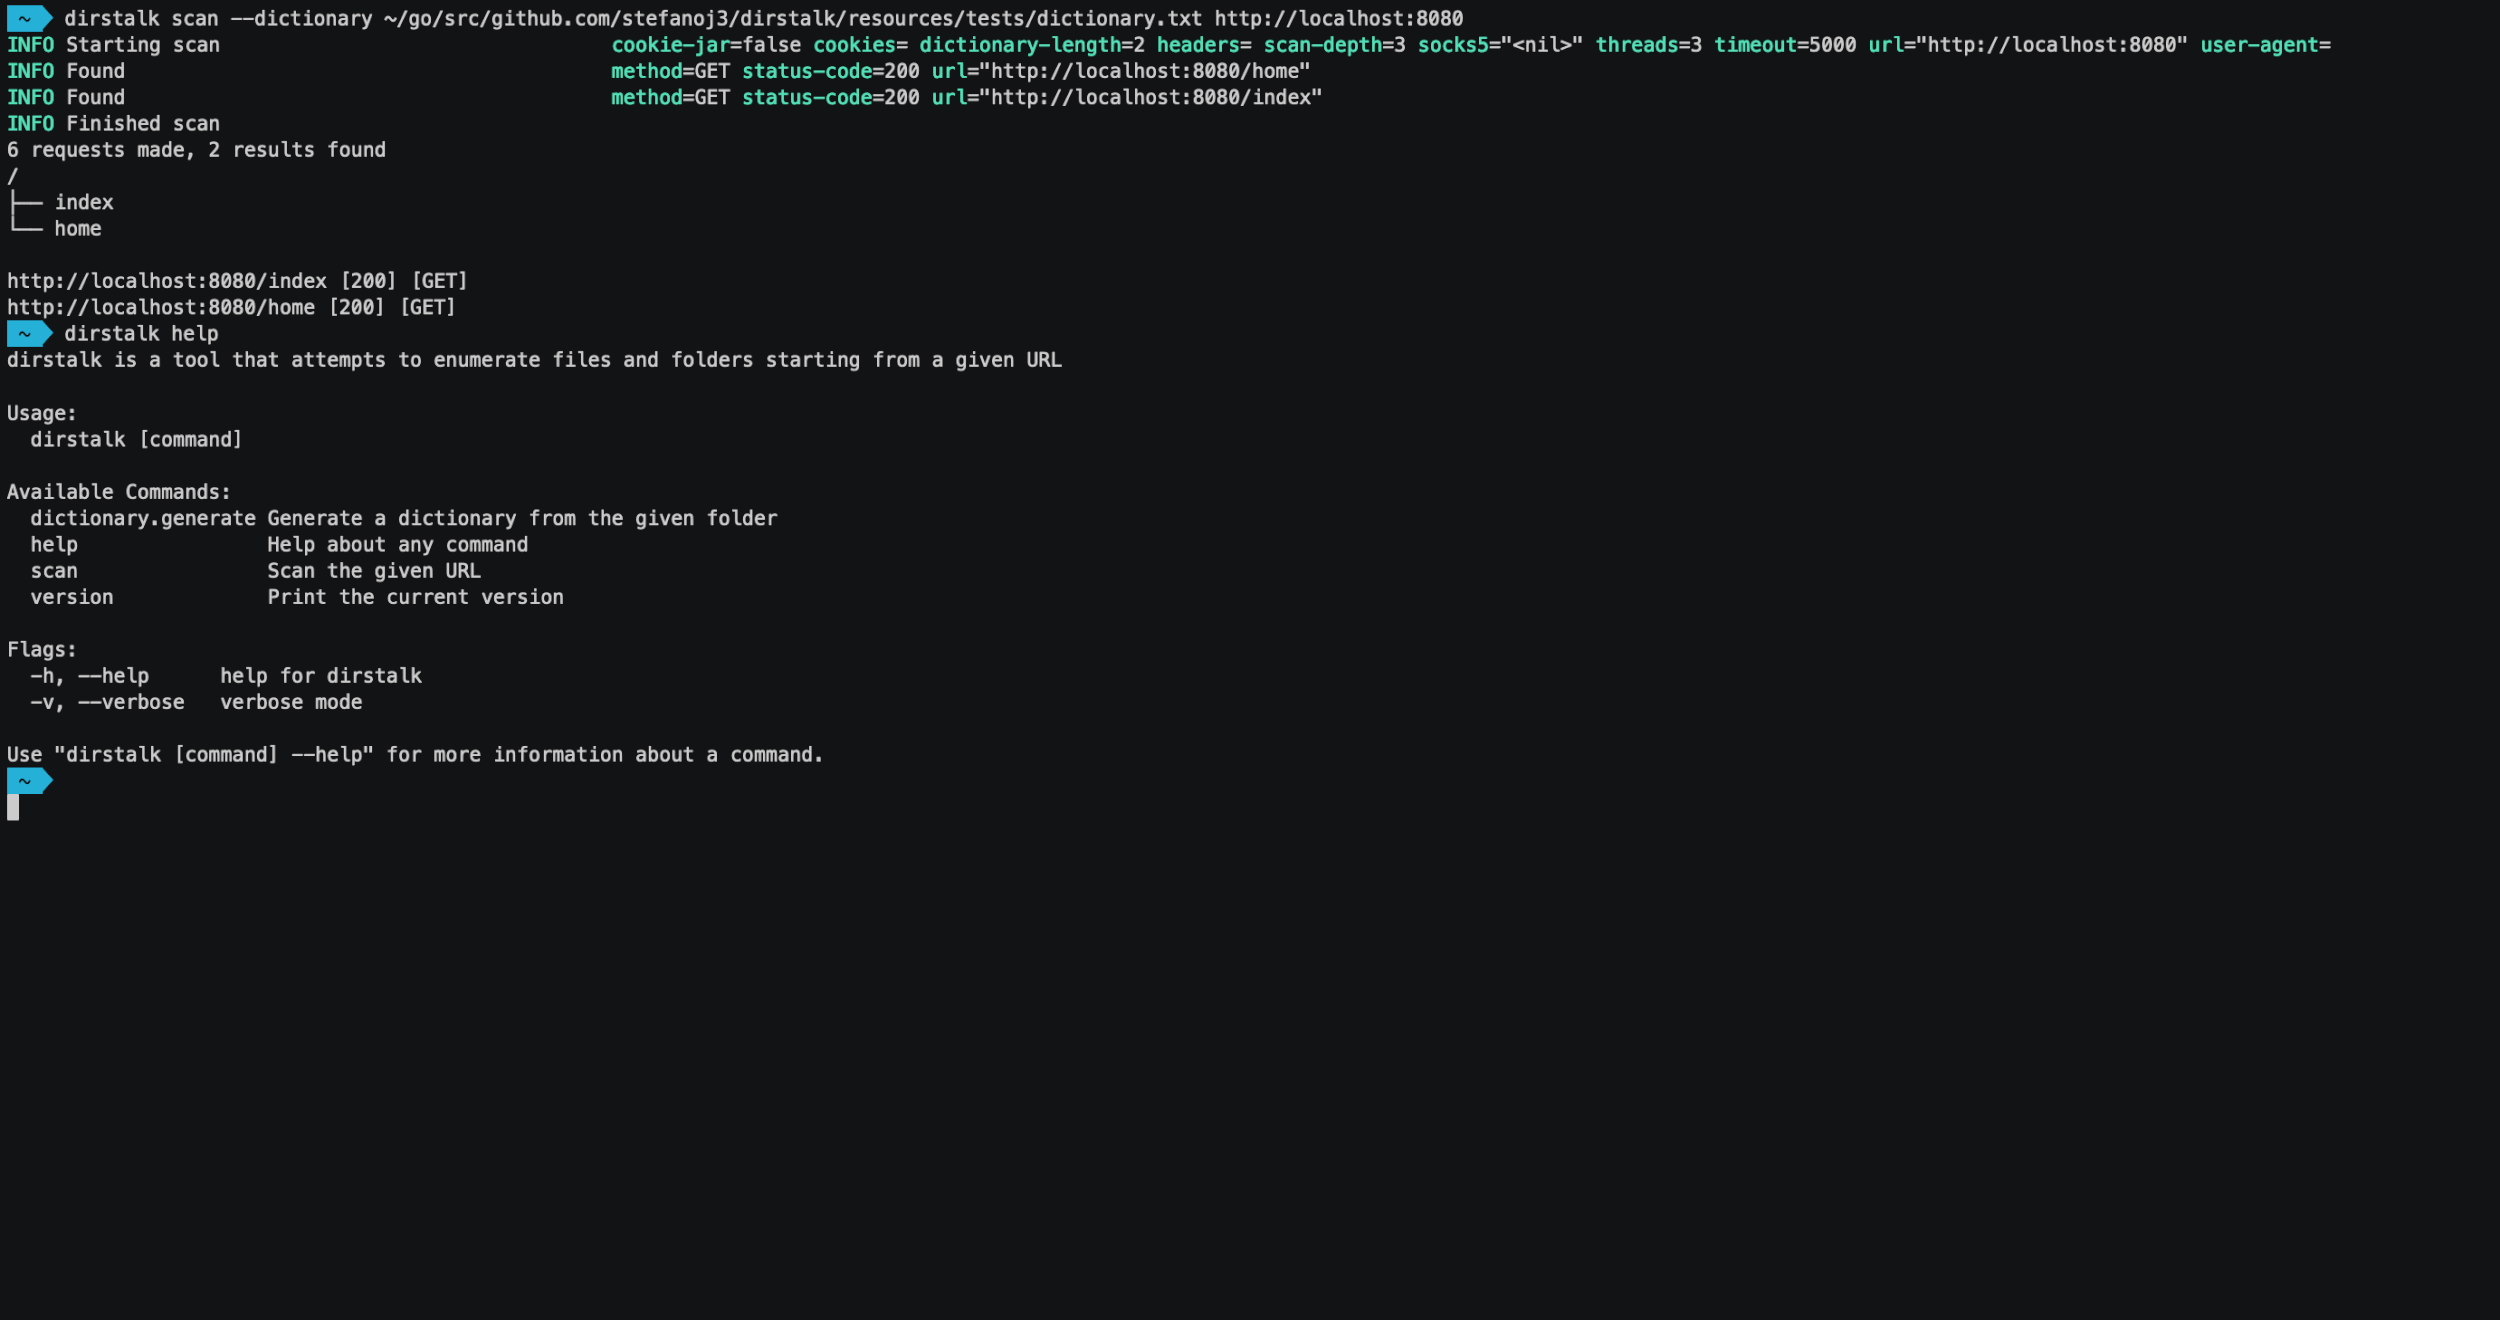
Multi threaded application designed to brute force paths on web servers.
An Internet Explorer post exploitation library.
Toolkit to detect and keep track on Blind XSS, XXE & SSRF.
HTTP parameter discovery suite.
Command-line script to test cloud storage for common misconfiguration issues.
Prevents you from committing secrets and credentials into git repositories.
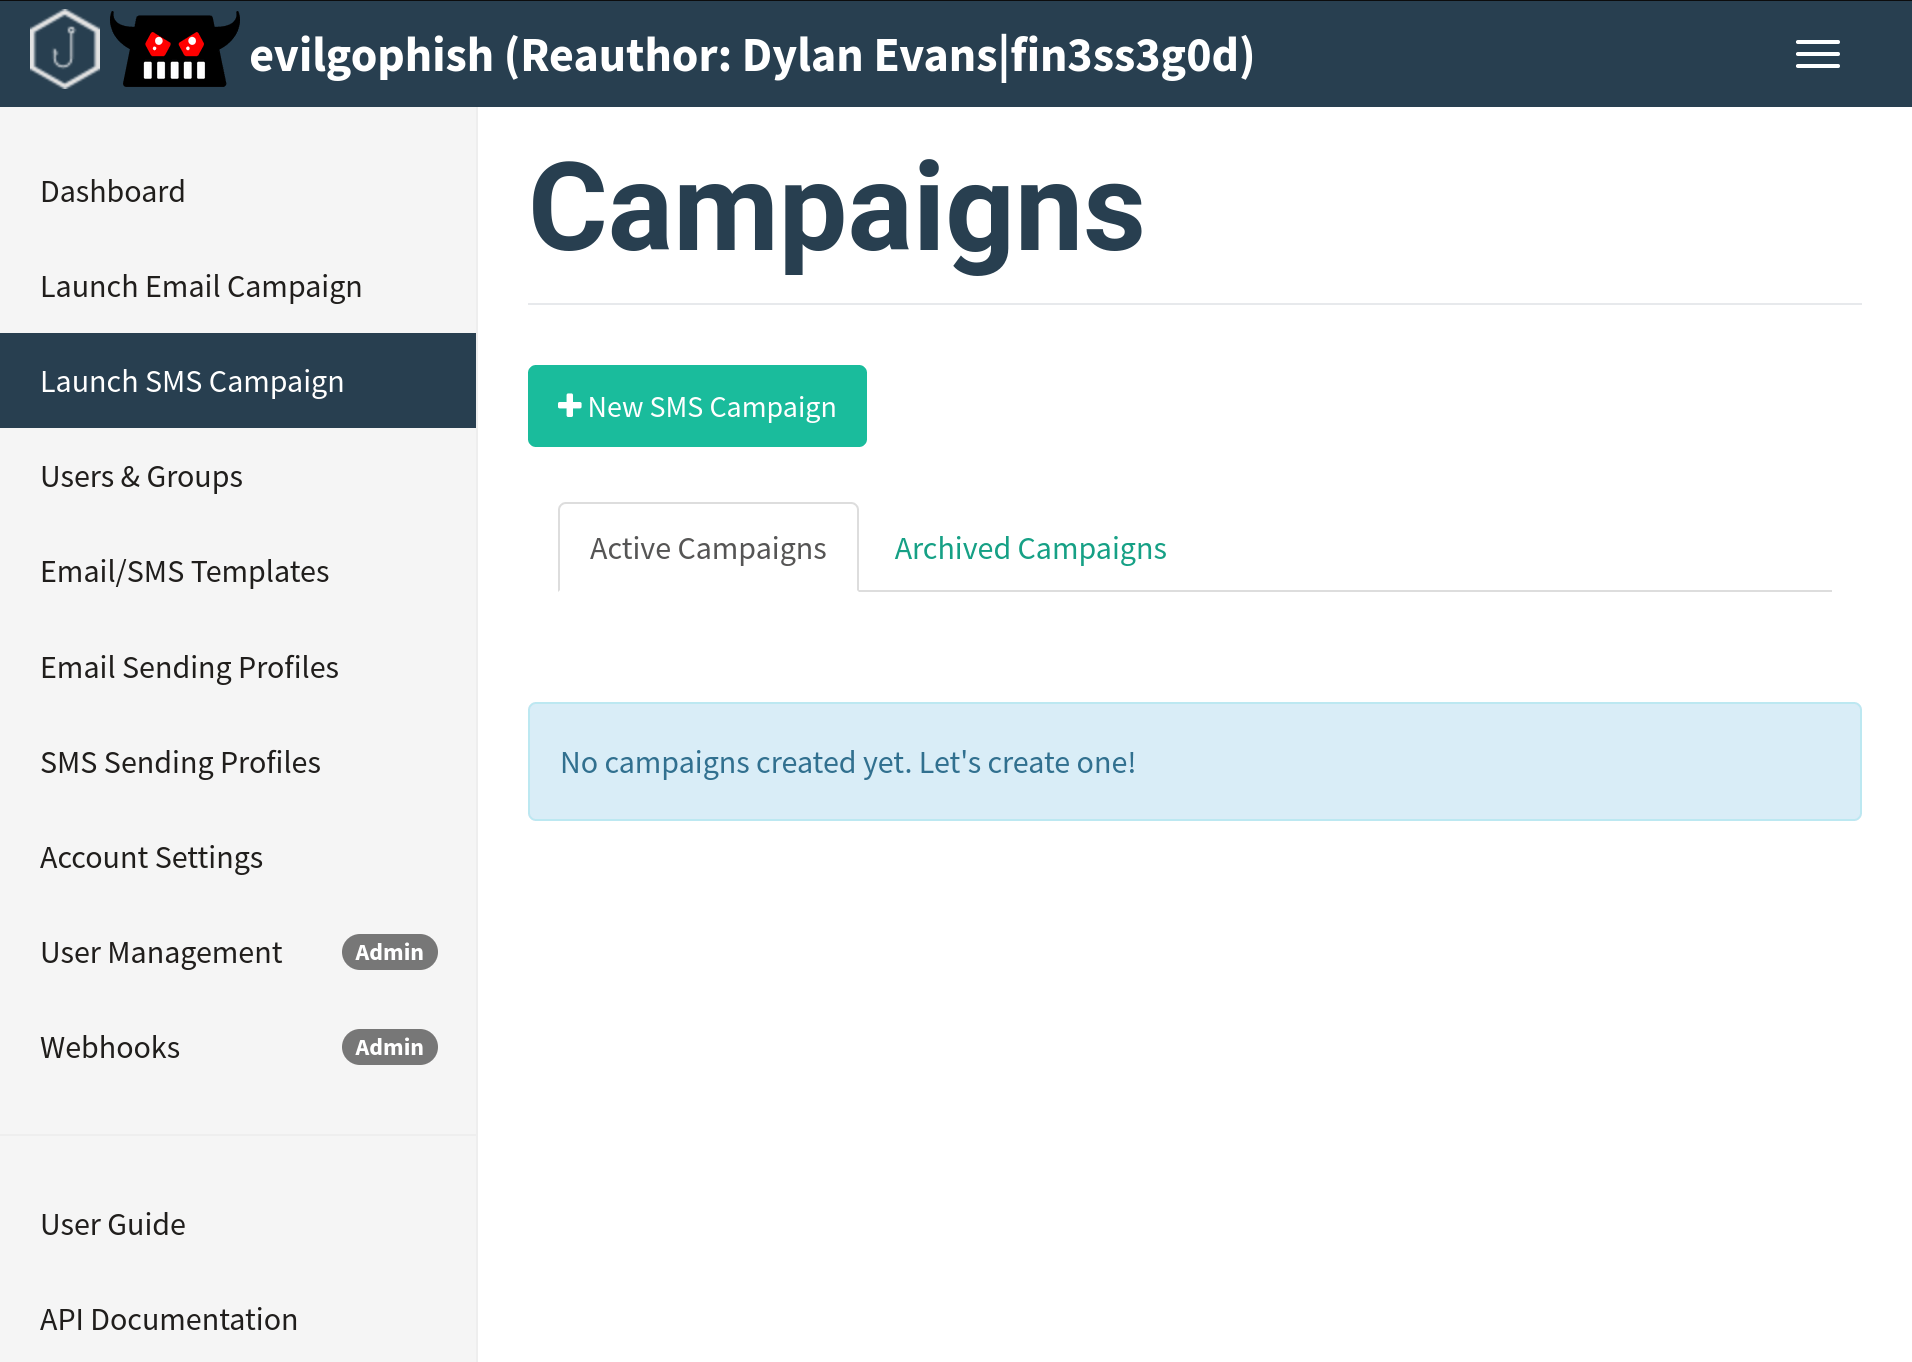
Combination of evilginx3 and GoPhish.
Specify targets and run sets of tools against them.
Reverse engineering and pentesting for Android applications.
Distribute the workload of many different scanning tools with ease.
A Burp Suite extension made to automate the process of bypassing 403 pages.
API key/token exploitation made easy.
Extract data from a .git directory.